AI Act compliance for AI Engine Pro builds
Written for people shipping chatbots, assistants and generators on WordPress with AI Engine Pro. What the Regulation asks of those builds, and what it does not.
A plugin build is still a system under the Regulation
The AI Act does not care whether you wrote a model or wired one up: it only cares what the resulting system does, who it affects, and whose name is on it.
You are usually the deployer
Running an assistant on your own site, under your own authority, in a professional capacity puts you in the deployer role, with duties on oversight, input data and telling people what they are dealing with.
Sometimes you become the provider
Shipping the build to a client under your own name, or changing what it is meant to do, can move you into the provider role. That is a materially heavier set of obligations, and a contract alone does not move it back.
Location is not the test
If the system, or what it produces, is used in the Union, the Regulation can reach you wherever the site is hosted and wherever you are established.
Risk first, then role
Start with what the system can do to people. The risk tier decides how much is at stake; the role decides who carries it. Doing it the other way round is how builds get misclassified.
Risk
Most AI Engine Pro builds sit at limited risk: they interact with people or generate content, so Article 50 transparency applies. Some sit lower. A few, typically where the output feeds hiring, credit, education or access to services, sit higher.
Role
Deployer for your own site, provider once it goes out under your name or you change its purpose. Agencies frequently hold both roles across different clients at the same time.
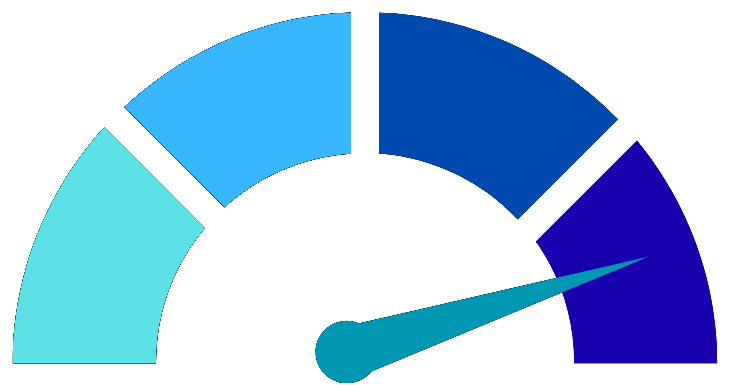
Compliance score
What you already have: the disclosure on the chat window, who reviews the logs, what happens when the assistant gets something wrong, and whether any of it is written down.
The routes described on this page are common cases, not conclusions. Every implementation needs its own analysis: the same plugin, configured differently, can land in a different tier with a different role attached.
What a compliant build looks like
For a typical limited-risk assistant. Most of it you can do inside AI Engine Pro itself, which is the point: the compliance work and the build live in the same place.
In the plugin
- A clear disclosure in the chatbot intro that the visitor is talking to AI, not a person.
- A system prompt that sets the assistant's scope and tells it to refuse what falls outside it.
- Conversation logging switched on, with a retention period you have actually decided.
- Marking on generated images or media, where the build produces them.
- Limits on any function calling: what it may touch, and what it may never do unattended.
On paper
- A note of the role and risk classification, and the reasoning behind it.
- Who is responsible for the assistant, and who reviews it when it misbehaves.
- The model and provider in use, and what happens to the data you send them.
- Evidence that the people operating it have been given guidance, under Article 4.
- For client work, which of you holds which role, agreed before launch rather than after.
None of this requires a separate compliance stack. The disclosure, the prompt scope, the logging and the retention are plugin settings. What AAMS adds is the classification, the reasoning and the documentation that makes it defensible.
If compliance is not where your priorities are right now
We are not going to pretend there is only one answer. The honest technical alternative to looking compliant while hoping nobody checks is to genuinely stop serving EU visitors.
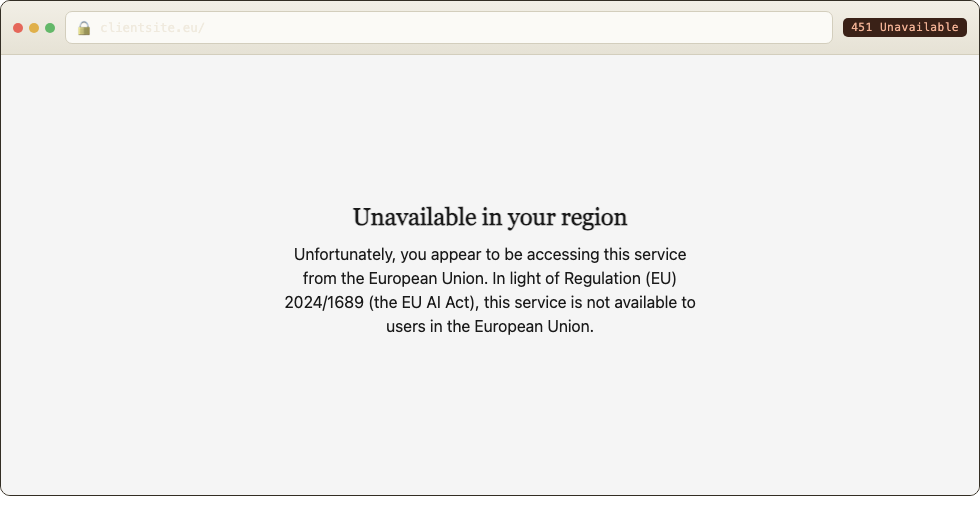
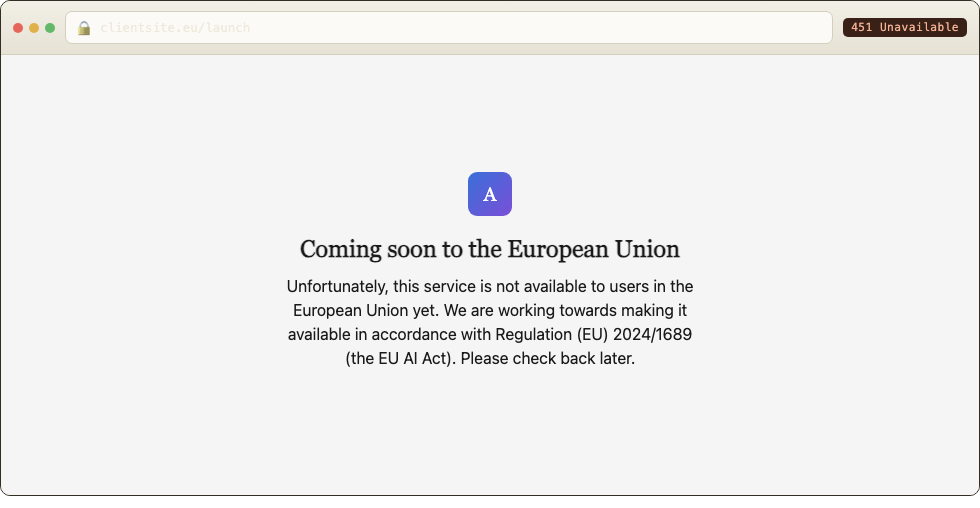
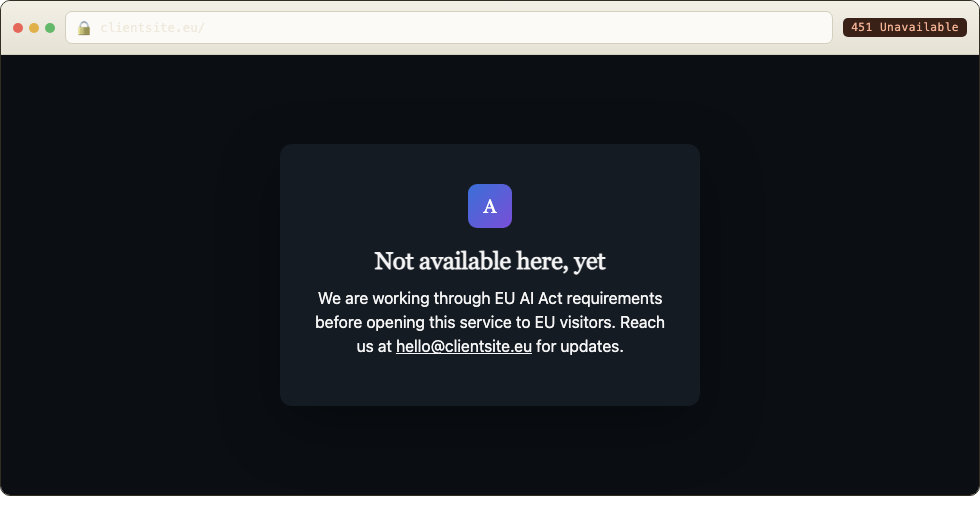
"Not in the EU (Yet)" is a small, standalone WordPress plugin we wrote and give away. It blocks public site and REST requests from EU IP addresses at the server level, using a country header supplied by a trusted CDN or host. No account, no email, no catch.
Its settings page offers three editable visitor notices: a formal legal notice, a message about the cost of excessive bureaucracy, and a plain "coming soon" notice, plus an optional logo, a custom HTML card and an opaque background style.
Download "Not in the EU (Yet)"
- Blocks public front-end and REST requests from EU IP addresses.
- Reads the country from a trusted CDN or host header; nothing is phoned home.
- Leaves wp-admin, AJAX, cron and WP-CLI open, so the site stays manageable.
- Free, self-hosted, and yours to keep. Deactivate it whenever you change your mind.
A technical access-control measure, not legal advice or a conclusion about your obligations. It requires country geolocation headers from your CDN or host.
Either path can lead back to the other. Deactivate the plugin whenever you are ready to serve EU users, and come back to RRCS when you want a structured read on what that involves.
The dates that matter
The Digital Omnibus changed when the high-risk rules arrive. The milestones already in force remain in place.
Updated for Regulation (EU) 2026/1744, published on July 24th, 2026-
AI literacy and prohibited practices The first prohibited-practice rules and the AI literacy framework began to apply.
-
Governance and GPAI obligations EU governance provisions and obligations for providers of general-purpose AI models became applicable.
-
Transparency and wider application Article 50 transparency duties and most remaining AI Act provisions apply, subject to the amended transitions.
-
Content marking transition and new prohibited practices The transition point for certain pre-existing generative systems and the new prohibited-practice provisions applies.
-
Stand-alone high-risk systems The high-risk rules for systems classified under Article 6(2) and Annex III apply.
-
High-risk systems in regulated products The high-risk rules for systems classified under Article 6(1) and Annex I apply.
Written by someone who uses the plugin
AAMS is run by qualified EU lawyers specialised in AI. It is also built on AI Engine Pro. The compliance questions on this page are the ones that came up in our own builds before they were ever client work.
Most AI projects we see online are not compliant, and the exposure is not only regulatory. European users have become genuinely attentive to how AI is disclosed, and a build that hides it carries a reputational cost as well as a legal one.
Related work
ChatLeg is an AI service for Italian lawyers, built on the same stack. It is in Italian, but it shows what the approach looks like in production.
chatleg.proAI Engine Pro is a third-party product. AAMS is not affiliated with it and speaks only for its own legal work.
Running a different AI plugin? See our general WordPress compliance page.
Find out where your build actually sits
Seven short steps. It asks what the assistant does, not who your clients are.